CVE-2026-80668 on CentOS 7: Fixed Kernel for EL7
CVE-2026-80668 is a remote Linux kernel use-after-free in netfilter conntrack, CVSS 9.8. The stock CentOS 7 kernel is affected with no update. The fix…
Practical Security guides from the GetPageSpeed engineering team: configuration, performance tuning and security for production Linux servers.
94 articles
CVE-2026-80668 is a remote Linux kernel use-after-free in netfilter conntrack, CVSS 9.8. The stock CentOS 7 kernel is affected with no update. The fix…
Remi stopped building PHP for CentOS 7 in June 2024. Here is how to keep your existing Remi PHP receiving security updates in place,…
CVE-2026-111497 (HTTP2Shell) is a Brotli decoder bug. ngx_brotli only compresses and is not affected; on CentOS 7 and Amazon Linux 2 the fix is…
PHP2Shell (CVE-2026-109618, CVE-2026-109619) is fixed in every AlmaLinux 8, 9 and 10 PHP stream. How to check your build, the fixed version per stream,…
PHP2Shell (CVE-2026-109618, CVE-2026-109619) has no distribution or upstream fix on CentOS 6. Here is the in-place fix for the stock PHP 5.3 and Remi…
CVE-2026-98432 is a remote Linux kernel use-after-free. CentOS 7's stock kernel is not affected; ELRepo's kernel-lt and kernel-ml are and get no fix. The…
PHP 8.2 reaches end of life on December 31, 2026: no more upstream security releases. Upgrade paths for current distros, and patched 8.2 packages…
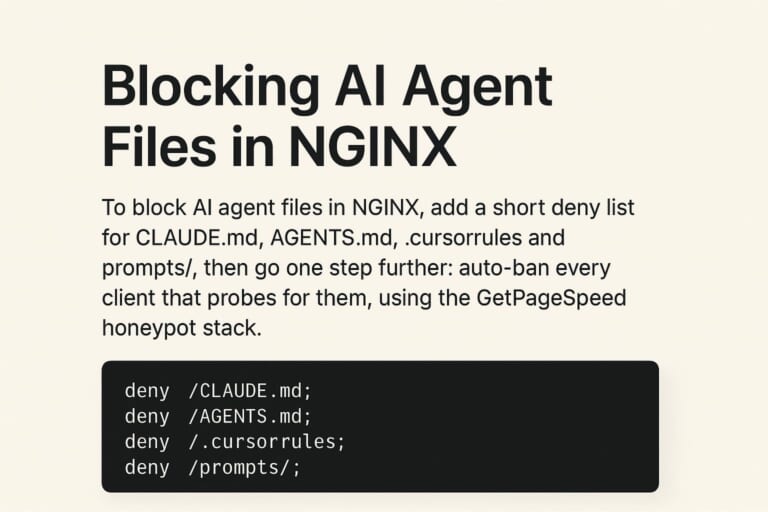
AI coding agents leave CLAUDE.md, AGENTS.md and prompt files in your web root. Block them in NGINX and auto-ban the scanners that probe for…
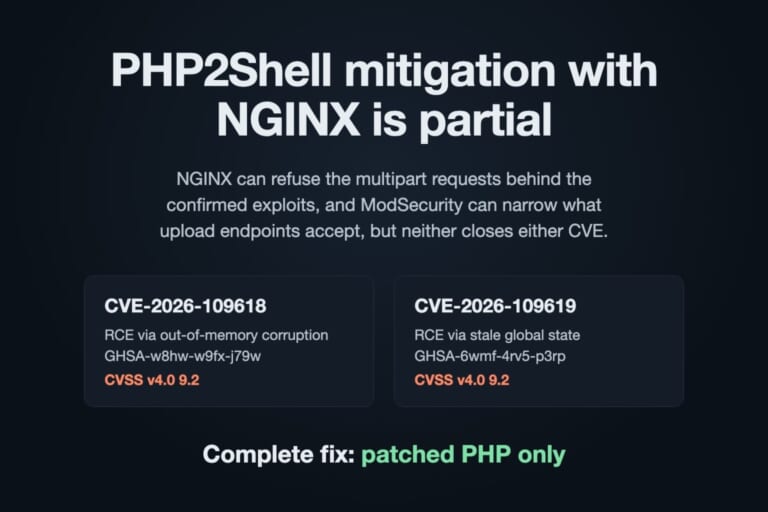
Can NGINX mitigate PHP2Shell (CVE-2026-109618, CVE-2026-109619)? Partly. Tested configs for blocking multipart and filtering uploads with ModSecurity, and why only patched PHP fixes it.
PHP2Shell (CVE-2026-109618, CVE-2026-109619) has no AWS fix for PHP 7.2 or 7.4 on Amazon Linux 2. Upgrade Amazon's php7.2 or Remi's php74 in place…