Remi PHP Extended Support: Security Updates for CentOS 7
Remi stopped building PHP for CentOS 7 in June 2024. Here is how to keep your existing Remi PHP receiving security updates in place,…
Practical php guides from the GetPageSpeed engineering team: configuration, performance tuning and security for production Linux servers.
23 articles
Remi stopped building PHP for CentOS 7 in June 2024. Here is how to keep your existing Remi PHP receiving security updates in place,…
PHP2Shell (CVE-2026-109618, CVE-2026-109619) is fixed in every AlmaLinux 8, 9 and 10 PHP stream. How to check your build, the fixed version per stream,…
PHP2Shell (CVE-2026-109618, CVE-2026-109619) has no distribution or upstream fix on CentOS 6. Here is the in-place fix for the stock PHP 5.3 and Remi…
PHP 8.2 reaches end of life on December 31, 2026: no more upstream security releases. Upgrade paths for current distros, and patched 8.2 packages…
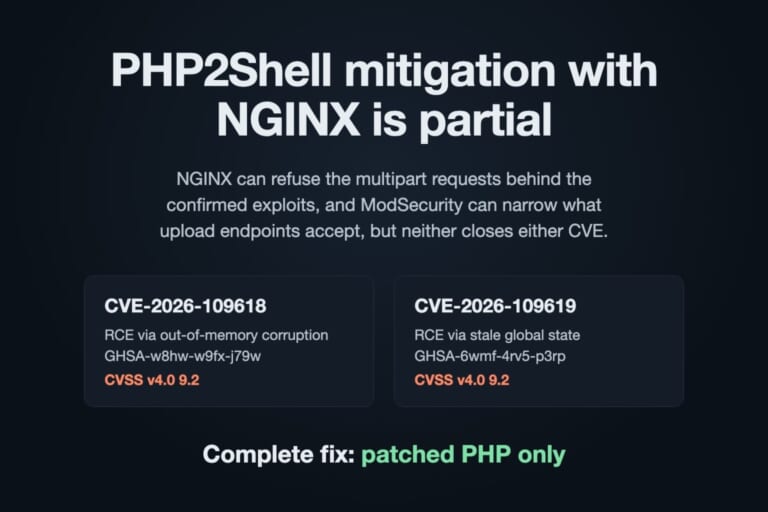
Can NGINX mitigate PHP2Shell (CVE-2026-109618, CVE-2026-109619)? Partly. Tested configs for blocking multipart and filtering uploads with ModSecurity, and why only patched PHP fixes it.
PHP2Shell (CVE-2026-109618, CVE-2026-109619) has no AWS fix for PHP 7.2 or 7.4 on Amazon Linux 2. Upgrade Amazon's php7.2 or Remi's php74 in place…
Install PHP 8.5 on CentOS 7 using base packages or a parallel collection, with PHP-FPM, built-in OPcache and clear extension compatibility guidance.
PHP2Shell (CVE-2026-109618, CVE-2026-109619) is a critical unauthenticated PHP RCE. Fixes for Ubuntu 20.04/18.04 and Debian 10 are Ubuntu Pro or ELTS only, and sury…
PHP2Shell (CVE-2026-109618, CVE-2026-109619) is a critical unauthenticated PHP RCE. Here is the free fix for every PHP from the stock 5.4 to 8.4 on…
Learn how to implement NGINX secure link functionality for signed URLs and hotlink protection. This comprehensive guide covers the HMAC Secure Link module installation,…